Repository navigation
Enable TLS 1.3 on the WS client for Overpass API requests - #1302
Merged
Merged
Conversation


|


jake-low
approved these changes
Oct 28, 2026
 jake-low
left a comment
jake-low
left a comment
Contributor
There was a problem hiding this comment.
I was super confused by this PR until I realized that WS in Play doesn't refer to WebSockets but to "Web Services", the default HTTP client. What a terrible name. 🙃
Anyway, LGTM. Hopefully this fixes the Overpass API issue; even if it does not, defaulting to TLS v1.3 and only using v1.2 as a fallback is a better behavior for all outbound HTTP requests we make.

This file contains hidden or bidirectional Unicode text that may be interpreted or compiled differently than what appears below. To review, open the file in an editor that reveals hidden Unicode characters.
Learn more about bidirectional Unicode characters
Sign up for free
to join this conversation on GitHub.
Already have an account?
Sign in to comment


Add this suggestion to a batch that can be applied as a single commit.This suggestion is invalid because no changes were made to the code.Suggestions cannot be applied while the pull request is closed.Suggestions cannot be applied while viewing a subset of changes.Only one suggestion per line can be applied in a batch.Add this suggestion to a batch that can be applied as a single commit.Applying suggestions on deleted lines is not supported.You must change the existing code in this line in order to create a valid suggestion.Outdated suggestions cannot be applied.This suggestion has been applied or marked resolved.Suggestions cannot be applied from pending reviews.Suggestions cannot be applied on multi-line comments.Suggestions cannot be applied while the pull request is queued to merge.Suggestion cannot be applied right now. Please check back later.
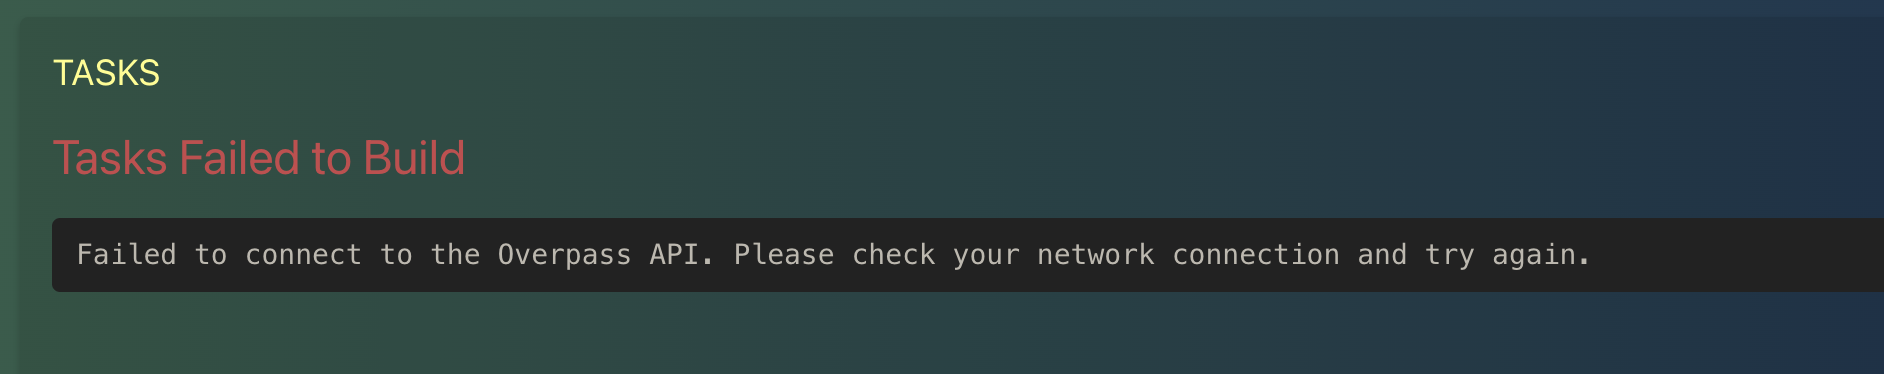
Overpass API endpoints have tightened their connection requirements, and outbound requests from the backend's Play WS client can fail during the TLS handshake. This sets TLS 1.3 as the WS client's preferred protocol, with TLS 1.2 still allowed as a fallback.
This is the error i was seeing and why i made the change. I didnt find anything online that said TLS requirements changed.